
SECURITY CONFIDENTIAL
Security Confidential S17 E9 Husam Shbib
This week on Dark Rhiino Security’s Security Confidential podcast, Host Manoj Tandon talks to Husam Shbib. Husam is a cybersecurity consultant specializing in penetration testing, digital forensics, malware analysis, programming, and OSINT. He holds multiple certifications, including ICMDE, CCE, CCD, CCDFA, IWM, 3CE/I, eCDFP, etc. He spoke at conferences and events such as BlackHat MEA, ASFSFM, 3D […]
Video
This week on Dark Rhiino Security’s Security Confidential podcast, Host Manoj Tandon talks to Husam Shbib. Husam is a cybersecurity consultant specializing in penetration testing, digital forensics, malware analysis, programming, and OSINT. He holds multiple certifications, including ICMDE, CCE, CCD, CCDFA, IWM, 3CE/I, eCDFP, etc. He spoke at conferences and events such as BlackHat MEA, ASFSFM, 3D Forensics, and others. He is committed to cybersecurity awareness, as he shares knowledge through LinkedIn, YouTube, and personal mentoring.
The Hacker's Playbook | Security Confidential
Chapter Titles:
00:00 Introduction
02:14 All hackers aren’t bad?
04:38 How is cybersecurity in the Middle East
06:03 To become an Ethical hacker, should you focus on penetration testing first?
07:14 How does a hacker’s mind work?
12:04 How do you not get discovered in the scanning phase?
14:16 Hackers prefer to work alone
15:10 Hackers aren’t using the same tools
19:05 If you want in, you could get in
28:57 Any companies that are well defended?
30:45 Air gapping correctly
39:10 More about Husam
Audio:
Spotify Embed: S17 E09 The Hacker’s Playbook
Important Links
Full Transcript
Manoj Tandon:
Hello everyone! This is your host, Manoj Tandon, with another episode of Dark Rhiino Security’s Security Confidential. Today we have an awesome guest joining us from halfway around the world. But before I get to him, please hit the Like and Subscribe buttons—it helps with the algorithm, and it tells us you still love us so we can keep bringing you great content. Without further delay, let me introduce you to Husam Shbib. He’s a cybersecurity consultant currently based in Saudi Arabia and a specialist practitioner. He focuses on penetration testing, digital forensics and malware analysis, programming, and OSINT (open-source intelligence). He holds multiple certifications, including ICMDE, CCE, CCD, and CCDFA, to name a few. He has spoken at Black Hat EMEA, ASF, SFM, 3D Forensics, and other conferences. He’s passionate about developing cybersecurity awareness and shares his knowledge on LinkedIn, YouTube, and through personal mentoring. Thank you so much, Husam, for joining us late in the evening from so far away.
Husam Shbib:
Thank you so much, Manoj. Thank you for having me. It’s an honor to be on Security Confidential. I’m really glad I can participate in such a great show.
Manoj Tandon:
Give us a little bit about your background. You’re the first person from the Middle East we’ve had on the show. How did you get into cybersecurity?
Husam Shbib:
It’s a long story. It started when I was in middle school. I was reading my IT book and saw a section about hackers—defined as “computer or network thieves.” I was fascinated by the term and how they were described. I started looking up more information about hackers and what they do. My teacher stopped me and said, “Husam, never look up hackers; they’re dangerous—don’t go near them.” That only made me more curious. I wondered, Are they really dangerous? Is that accurate? My journey started there, in seventh grade, teaching myself cybersecurity.
Manoj Tandon:
And you had no guidance other than yourself—you learned step by step?
Husam Shbib:
None at all. It was a very niche area; no one was talking about cybersecurity, hackers, hacking, or even information security. For me, it felt like a new domain I could pursue. The curiosity was unlike anything else. There was so much to learn, and it felt like an ocean with no guidance or mentors. You had to solve problems yourself. There were very few YouTube videos back then. I was hunting for CDs, which were rare. Friends would say, “Go to this place, turn right, turn left,” and sometimes you’d still never find what you needed.
Manoj Tandon:
Is that still true today in the Middle East?
Husam Shbib:
No—the complete opposite. Today there’s too much information. The challenge is figuring out the real, trusted sources. With so many options, people get confused about where to learn.
Manoj Tandon:
What priority is cybersecurity getting from companies in the Middle East right now?
Husam Shbib:
A lot of attention. We know this era is a cyber era. Communication, intelligence, and decision-making are increasingly cyber-driven—cyber threat intelligence, for example. You see a lot of APTs (nation-state groups) doing things remotely that once seemed impossible—think Stuxnet-style impacts. That’s why countries invest heavily. Saudi Arabia is among the leading countries investing in cybersecurity development.
Manoj Tandon:
Aramco had breaches a decade or so ago involving their safety systems.
Husam Shbib:
Yes—Shamoon. I believe around 2018. Aramco was hit by a very destructive malware family. Even before that, there was a push to develop cybersecurity, but incidents accelerate the realization: you need faster and better development to defend against ransomware gangs, APTs, and other threats. You need capabilities to defend, track, and prevent.
Manoj Tandon:
It’s always good to have indigenous resources that can provide strong protection. That’s the closest you can get to trust in this business.
Husam Shbib:
For sure. You need to protect customers and systems—and, at a national level, protect the country from threat actors.
Manoj Tandon:
You’ve done a lot of penetration testing. You became an ethical hacker despite your teacher’s warning.
Husam Shbib:
Exactly.
Manoj Tandon:
Many people say, “I’m going to be an ethical hacker.” Knowing what you know now, is that where you’d advise someone to start? Or should they be a SOC analyst, auditor, or blue teamer?
Husam Shbib:
I’ve been an auditor, a penetration tester, and now I’m in digital forensics. I still advise starting with penetration testing. With the attacker’s mindset, you learn where attackers go, how they pick targets, and which vulnerabilities or misconfigurations they exploit. That prepares you for many paths—continuing in pentesting, advancing to red teaming (the pinnacle of offensive work), or moving into SOC/GRC. The technical foundation helps everywhere.
Also, searching is a critical skill. People rely on tools like ChatGPT for everything, but I’ve seen LLMs give false information. They’re trained on data and can miss things. Prompt engineering helps, but you can’t depend on LLMs alone. Strong research habits are still essential.
Manoj Tandon:
Walk us through how a “bad guy” behaves when targeting a random company. How do they go about it?
Husam Shbib:
If I’m a bad guy with no ethical boundaries and I’m targeting “Company XYZ,” I invest a lot of time in reconnaissance—open-source intelligence on social media, archived websites, anything public. I’m not scanning yet; I’m just gathering information: employee names, email naming conventions, domains, IPs, email gateways—every byte that could be useful later. If it’s a big target, I might look on the dark web for data being sold to use in later stages.
After reconnaissance comes scanning. With the information gathered, I scan what matters—web apps, infrastructure, networks. I look for vulnerabilities and misconfigurations I can exploit to gain access. This is usually black-box: I don’t have source code or internal network maps. I infer from responses—maybe a web application firewall blocked something, so I try different payloads or vectors to bypass filters. I enumerate tech stacks, operating systems, and languages, because exploitation differs (e.g., SQL injection vs. XSS). I also keep an eye on OS-level vulnerabilities and widely used components.
Manoj Tandon:
Are you looking for domains, servers, admin credentials—what specifically?
Husam Shbib:
Domains, IPs, subnets—all that begins in recon. In scanning, I probe the application and infrastructure: test for SQL injection, XSS, and other issues. If I successfully phish a user and get credentials, internal network access opens up, and then it becomes network hacking—enumeration, lateral movement, privilege escalation.
Manoj Tandon:
Most vulnerabilities aren’t patched.
Husam Shbib:
Often attackers repurpose old vulnerabilities into “new” zero-days by modifying them. Some true zero-days get sold on the dark web—expensive, but worthwhile for certain groups because the ROI from ransomware or access resale can be high.
Manoj Tandon:
How do you avoid detection during scanning?
Husam Shbib:
That’s what separates elite hackers from the rest. Elite operators blend into normal traffic and obfuscate their traces and payloads. Solutions get smarter, but humans do too. Next-gen firewalls, IDS/IPS, EDR/XDR—all can be bypassed. Attackers look for the weakest link. Many major corporations with top-tier tools still get breached, sometimes going months before discovery. For high-value targets, elite teams may spend six months just on recon and scanning.
Manoj Tandon:
So they’ll want a big payout.
Husam Shbib:
Exactly—especially if sponsored. Teams combine different skill sets to complement each other. Some individuals can reverse-engineer entire security products alone. Fortunately, many of them work on the ethical side.
Manoj Tandon:
Do elite hackers build custom payloads or use off-the-shelf tools?
Husam Shbib:
Off-the-shelf gets detected quickly. Tools like Mimikatz are widely known and flagged. Serious actors craft their own tooling, minimize suspicious API calls, encrypt or stage code, and tailor payloads to what recon reveals—even details the company’s own IT/Sec team may have missed. Orphaned accounts and unmanaged devices are common. I’ve seen user access reviews where accounts of resigned employees remain active.
Manoj Tandon:
Onboarding is easy; offboarding is hard.
Husam Shbib:
Exactly—“orphan accounts.” With an active account, I can impersonate a legitimate user. Once I get a foothold—this is exploitation—I can encounter an Active Directory environment and start moving toward domain admin or even enterprise admin. Then I can access sensitive docs, move laterally across subnets, and, if my goal is ransomware, disable backups and make recovery painful. The specific goal is typically defined before recon starts.
Manoj Tandon:
Given all that, if a company invests in expensive tools and defense-in-depth, can a determined attacker still get in? What percentage of protection is realistic?
Husam Shbib:
There’s no such thing as 100%. Even with best practices and principles, humans can be socially engineered—or bribed. With enough time, attackers can find a zero-day unknown to the vendor. Even security products themselves get zero-days. Vendors urge rapid patching for a reason. If security tools are vulnerable, imagine the broader environment.
Manoj Tandon:
Websites and databases often aren’t well protected.
Husam Shbib:
Right. I’ve done pentests in environments where testing had to be on production—not ideal. You should test in a mirror/staging environment, then roll fixes to prod. On production, you must be extremely careful not to disrupt business. Attackers won’t be so considerate.
Manoj Tandon:
So after exploitation and in a stealthy red-team scenario?
Husam Shbib:
In red teaming, only a few senior stakeholders know it’s happening. You must stay stealthy—unlike pentesting where generating noise is acceptable. After exploitation, you enumerate again with your new access: find more users, vulnerabilities, protocols to abuse, and pivot until you hit the objective—whether that’s ransomware, data exfiltration, or something else.
Manoj Tandon:
Penetration tests are time-boxed, so effectiveness is limited.
Husam Shbib:
Exactly. Pentests are often one–two weeks—enough to find and validate many issues, but not to mirror a determined adversary. Red-team engagements may run 1–6 months, with specific goals. Multiple operators collaborate, and the longer timeline better simulates real-world attacks.
Manoj Tandon:
Have you ever found a company so well defended you’d “move on” if you were a criminal?
Husam Shbib:
Unfortunately, every company I’ve assessed had at least medium-to-critical issues. Sometimes I’ve found zero-days in private internal apps.
Manoj Tandon:
What should companies do? Segment the network? Partition high-risk users?
Husam Shbib:
Segmentation is essential, but in PCI DSS pentests we often find segmentation isn’t truly enforced—segments that shouldn’t talk to each other still can. Controls must be validated.
Manoj Tandon:
What about air-gapping?
Husam Shbib:
Air-gapped networks can still be compromised—Stuxnet is the classic example, with USBs bridging the gap. The attack surface is huge, so reduce it as much as possible. OT environments often run legacy systems full of known vulnerabilities. Organizations say they can’t patch or replace them due to operational risk and interdependencies.
Manoj Tandon:
Then what happens when a hacker exploits and shuts it down?
Husam Shbib:
Exactly. We’ve seen it happen, and it can happen again—especially with insider threats. Insiders know the environment and can blend in more easily.
Manoj Tandon:
You’ve seen insider incidents?
Husam Shbib:
Yes. As a digital forensics examiner, I’ve investigated insider exfiltration cases. Our job is attribution: who did it, how, when, why, and what they did. You may need more data sources—disk images, memory captures, network packets. Unfortunately, some responders power machines off, losing volatile memory. If drives are encrypted and users won’t provide passwords, analysis can become much harder. Call forensics early and preserve evidence correctly.
Manoj Tandon:
Attribution is hard—why?
Husam Shbib:
Because sophisticated actors use advanced techniques to hide tracks, and if critical evidence (like memory or network data) isn’t captured, you’re limited to disk artifacts. That makes timelines and definitive conclusions more difficult, though not impossible with the right data.
Manoj Tandon:
We’ll need you back to talk solely about digital forensics—we’re at the hour and just scratched the surface.
Husam Shbib:
Sure—happy to!
Manoj Tandon:
Before we wrap, anything to plug? Any upcoming talks?
Husam Shbib:
Hopefully next month I’ll be giving a virtual talk at BFIC, and later this year I’ll be at Black Hat Middle East and Africa in person. BFIC is virtual; Black Hat MEA is in person.
Manoj Tandon:
Fantastic. Send us the link to the paper you’ll be presenting at Black Hat, please.
Husam Shbib:
Hopefully—sure.
Manoj Tandon:
This was fascinating, Husam. It’s great to hear the depth of what it really takes to do these things. I’m sure our audience learned a lot, and we appreciate you sharing.
Husam Shbib:
I appreciate you having me. It was a really interesting conversation. I didn’t even notice an hour had passed! Thank you so much, and I look forward to future conversations.
Manoj Tandon:
Oh, we will. I’ll have Emily reach out to schedule more time—we need to take this further. Husam, thank you so much for being on the show. It was our honor and privilege.
Husam Shbib:
The honor is mine. Thank you, Manoj. Really appreciate it. Thank you.
Read more about Husam on his LinkedIn
Check out the other episodes in Season 17:
Ep. 0 Jon DiMaggio – Tracking Cyber Criminals
Ep. 1 John Carse – Why Your Browser Is Your Biggest Risk
Ep. 2 Alex Sharpe – Is Your Job Safe From AI?
Ep. 3 Chuck Brooks – Thinking Beyond the Checkbox
Ep. 4 Henrik Parkkinen – Adapting to AI & Rethinking What We Protect
Ep. 5 Alex Sharpe – Are AI Models Being Trained with Lies?
Ep. 6 Santosh Kaveti – Disaster Recovery Isn’t Optional
Ep. 7 Bob Burke – Think MFA is Enough? Think Again.
Ep. 8 Ed Gaudet – The Biggest Mistakes in Healthcare Security
Ep. 9 Husam Shbib – The Hacker’s Playbook
Ep. 10 Shayla Treadwell – The Psychology Behind Cyber Resilience
About Husam
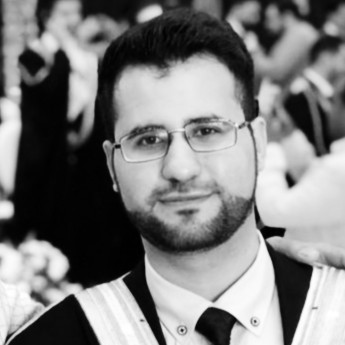
Husam Shbib is a professional cybersecurity consultant with deep expertise in penetration testing, digital forensics, malware analysis, programming, and OSINT.
He is the founder of the Memory Forensic website and holds numerous industry certifications including ICMDE, CCE, CCDFA, 3CE, and eCDFP, demonstrating his dedication to staying at the forefront of cybersecurity best practices.
Beyond consulting, Husam is a passionate advocate for cybersecurity education—he’s spoken at major conferences like BlackHat MEA, ASFSFM, and 3D Forensics. His commitment to digital safety extends to younger audiences through his storybook, Captain Cyber and the Safe Surfing Adventure, which teaches children about online safety in a fun and accessible way.
He actively mentors aspiring professionals and shares insights on platforms like LinkedIn and YouTube. Husam’s work blends technical precision with a mission to raise cybersecurity awareness in local and global communities alike.
About Us:
Dark Rhiino Security’s Security Confidential is a weekly Cybersecurity podcast where Host, Manoj Tandon, talks to Infosec and Cybersecurity professionals about the current issues going on in our industry. Guests are able to share their stories about how they began their journey into cybersecurity and connect with our audience. Listeners are able to tune in through Spotify, Apple Podcasts, Google Podcasts, Amazon Music, iHeartRadio, Youtube, LinkedIn, and more.
For inquiries, please email media@darkrhiinosecurity.com
Share and spread the word!
Archive source: Original website record. Original wording and artwork retained.