
SECURITY CONFIDENTIAL
Security Confidential S17 E0 Jon DiMaggio
This week on Dark Rhiino Security’s Security Confidential podcast, Host Manoj Tandon talks to Jon DiMaggio. Jon is the Chief Security Strategist at Analyst1 with over 15 years of experience tracking cyber threats. Specializing in enterprise ransomware and nation-state attacks, Jon is best known for infiltrating the LockBit ransomware gang during a two-year undercover operation. His research, […]
Video
This week on Dark Rhiino Security’s Security Confidential podcast, Host Manoj Tandon talks to Jon DiMaggio. Jon is the Chief Security Strategist at Analyst1 with over 15 years of experience tracking cyber threats. Specializing in enterprise ransomware and nation-state attacks, Jon is best known for infiltrating the LockBit ransomware gang during a two-year undercover operation. His research, including Ransomware Diaries and The Art of Cyberwarfare, has aided law enforcement and been featured by CBS 60 Minutes, The New York Times, and Wired. A frequent speaker at RSA, he has twice received the SANS Difference Makers Award for his groundbreaking work.
Tracking Cyber Criminals | Security Confidential
Chapter Titles
00:00 Introduction
02:34 You don’t need an expensive university
11:00 In order to be successful in cyber, you need to…
17:38 What are the bad guys doing?
23:13 What does the government do to help?
26:24 Consequences for bad actors
41:35 The Art of Cyber Warfare
44:05 Jon’s new book
Audio
Spotify Embed: S17 E0 Tracking Cyber Criminals
Important Links
Transcript
Manoj Tandon: Hello everyone, this is your host, Manoj Tandon. Welcome to another episode of Dark Rhiino Security – Security Confidential. Today, we have a celebrity guest joining us. But before I introduce him, please hit the like and subscribe button. We all work for the algorithm—so help us keep bringing you great content and fantastic guests like the one we have today. Our guest is none other than Jon DiMaggio. Many of you in cybersecurity already know him, but for those outside the field, Jon is the Chief Security Strategist at Analyst1, with over 15 years of experience tracking cyber threats. You may know him from his two-year undercover infiltration of the LockBit ransomware gang, his Ransomware Diaries volumes, or his book The Art of Cyberwarfare. He’s been featured on 60 Minutes, in The New York Times, Wired, and is a regular speaker at RSA. We’re honored to have him here. Jon, thank you so much for joining us today.
Jon DiMaggio: Thanks, Manoj. I really appreciate the kind words—and it’s great to be here.
Manoj Tandon: Well, I love saying kind words about other people—it’s my way of living vicariously. Let’s start with your origin story. How did Jon DiMaggio become the name everyone knows in cybersecurity?
Jon DiMaggio: It’s been quite a journey. I barely graduated high school with a 1.9 GPA—college wasn’t in the cards for me then. So I joined the Army and became a military policeman. I was lucky to work with the Criminal Investigation Division, doing undercover work in my early twenties. That experience taught me a lot about human behavior and risk. When I left the military, I wanted to become a police officer or join the FBI, but I had visible tattoos, which was frowned upon back then, and the FBI had a zero-tolerance policy for prior marijuana use. So I swallowed my pride, worked at Home Depot pushing carts, and used my GI Bill to take IT certifications.
The dot-com bubble had just burst, and I was buying cheap servers to build a home lab. That led to a help desk job doing network security, which opened the door to government work. I eventually became an intelligence analyst focused on espionage and signals intelligence. By 2014, I moved to the private sector—joining Symantec’s Attack Investigation Team, where I worked with some of the brightest minds I’ve ever met. After seven years, I joined Analyst1 in 2020. At first, I had no fancy data tools—just a laptop. Ransomware was exploding, and I realized I could directly talk to criminals on the dark web, just like victims do. That’s what led me to infiltrate LockBit and write The Ransomware Diaries.
Manoj Tandon: That’s a fascinating arc—from the military to intelligence to going undercover in the cyber world. You mentioned that 1.9 GPA earlier. With all the talk today about elite universities, what do you say to someone who didn’t go to MIT or Stanford but wants to break into cybersecurity?
Jon DiMaggio: Some of the smartest people I know didn’t come from elite universities—they came from hunger and hardship. When you’ve struggled to put food on the table, you get motivated to succeed. I’m not against higher education at all—it just wasn’t for me. I have learning disabilities and learn best hands-on. So I taught myself, spent nights and weekends studying while my friends were watching football. That drive can’t be taught—it comes from wanting a better life.
Manoj Tandon: That’s a great message. We’ve seen the same thing—talent can come from anywhere if the will is there.
Jon DiMaggio: Exactly. I once worked with a researcher who was doing incredible ransomware analysis work. Later I found out he was 17—and had started at 14! That’s the kind of curiosity and motivation we need in this field.
Manoj Tandon: Let’s talk about skill sets. If you broke cybersecurity down into three pillars—technical knowledge, human understanding, and business acumen—what’s the right mix?
Jon DiMaggio: I’d say 50% technical education—you must understand how systems work if you want to protect them or exploit them. About 30% should be business sense—you need to understand how organizations make money, build teams, and market ideas. And 20% is human intelligence—empathy and people skills. At the end of the day, we’re protecting people from people. Understanding motivation, psychology, and teamwork makes you far more effective.
Manoj Tandon: That’s solid advice. Now let’s shift to the juicy part—how does someone infiltrate a ransomware gang like LockBit?
Jon DiMaggio: It started with research. I mapped out their communication spaces on the dark web—where they talked, who their partners were, who sold them tools. I built personas and applied to join the gang when they were recruiting. I pretended to be a young, eager hacker. Because I knew their primary language was Russian and their English was poor, I spoke to them in German—forcing us to use broken English instead of translators. It worked. I didn’t make the final cut, but they didn’t forget me. When my report went public, they started using my picture as their avatar! So I reached out as myself, expecting hostility—but instead, they loved the attention. They’d joke with me, even praise me. For about a year and a half, we had regular contact—sometimes friendly, sometimes cat-and-mouse.
Manoj Tandon: That’s wild. They must have wanted the publicity too.
Jon DiMaggio: Definitely. It gave them notoriety, which they crave. For me, it gave insight into their mindset and operations. They assumed I’d only repeat what they told me, but I also dug into their networks, technical data, and associates. I’d piece together enough clues to paint a full picture—and publish it.
Manoj Tandon: At a technical level, what are ransomware gangs actually exploiting?
Jon DiMaggio: Two main things: vulnerabilities in infrastructure and vulnerabilities in people. They know large organizations have sprawling networks, and somewhere, something will be unpatched. But they also exploit humans—it’s often easier to trick someone than to hack a system. The combination is lethal. I often compare ransomware to the war on drugs—we talk big, but we do little. Attackers have both technical and psychological leverage.
Manoj Tandon: Why can’t we just stop the encryption process before it starts?
Jon DiMaggio: Because the top ransomware groups are run by world-class hackers. LockBit, for example, made over $100 million a year for three consecutive years. They reinvested that money like a legitimate company—adding automation, GUIs, and user support for their “affiliates.” It became a franchise model. They built tools so even low-skilled hackers could launch advanced attacks. The result was scale. Skilled operators still develop exploits on the fly, but automation made their reach enormous.
Manoj Tandon: What about defense? Couldn’t software companies like Microsoft or Oracle design inherently ransomware-resistant systems?
Jon DiMaggio: They try. Security is a huge priority for major vendors. But complexity and scale are enemies of perfection. You can’t control how customers configure your software. Security, usability, and accessibility are always in tension. The easier a product is to use, the harder it is to secure. Even if vendors patch vulnerabilities immediately, organizations often delay patching due to compatibility testing. That delay creates an attack window.
Manoj Tandon: Fair point. So how does our government handle it—particularly for military communications?
Jon DiMaggio: Government systems prioritize security over convenience. When I worked for intelligence agencies, every access required physical checks and multiple safeguards. Many systems are air-gapped—completely isolated from the internet. That’s why those networks are far harder to compromise. The weak links are often contractors and third-party vendors, not the core systems. The private sector can’t easily adopt those models because they prioritize profit and accessibility.
Manoj Tandon: So convenience still wins over security in most businesses.
Jon DiMaggio: Yes—and that’s why I say ransomware is our version of the war on drugs. We’re fighting it, but losing ground.
Manoj Tandon: Partly because large corporations don’t face consequences. Small businesses fold; big ones just pay the ransom.
Jon DiMaggio: Exactly. Look at the Change Healthcare breach. They paid $22 million to BlackCat to prevent data leaks. Then the hacker who didn’t get his cut went to another group—RansomHub—and extorted them again for another $22 million. Forty-four million dollars straight into the criminal economy. If they’d invested that in security, they’d have avoided it entirely.
Manoj Tandon: And some of that money likely came from federal grants or insurance anyway.
Jon DiMaggio: Right. It’s infuriating. Hospitals claim they’re broke, but they find millions to pay ransoms. Meanwhile, they deny patients essential care or skimp on security budgets.
Manoj Tandon: Couldn’t they build redundancy systems—mirror sites or rapid failover—to restore operations faster and avoid paying?
Jon DiMaggio: Yes, with investment. Full instant recovery isn’t realistic, but strong backup systems and clear restoration playbooks can minimize downtime. Companies are improving there—that’s why ransomware gangs now steal data before encrypting it. They know backups have gotten better.
Manoj Tandon: What was your biggest revelation from the LockBit operation?
Jon DiMaggio: That these criminals are still human. Some of them, under different circumstances, could’ve been working alongside us. I even befriended one hacker who later warned me about planned hospital attacks. His tip allowed us to alert law enforcement and stop them. That’s the power of combining human intelligence with technical intelligence.
Manoj Tandon: That’s incredible. Did he ever consider turning good?
Jon DiMaggio: I tried. His name was Ivan, aka “Bastar Lord.” He was later indicted. I encouraged him to walk away, but he believed he’d never be caught. Now he’s sanctioned, can’t access his money, and can’t leave Russia. His story shows that cybercrime’s “riches” are usually an illusion.
Manoj Tandon: How much of ransomware today is state-sponsored?
Jon DiMaggio: It’s hard to quantify, but significant. The Russian FSB often coerces known hackers—offering protection or money in exchange for working on state objectives like cyberespionage or attacks against Ukraine. It’s a symbiotic, if dark, relationship.
Manoj Tandon: And of course, we hack too.
Jon DiMaggio: Of course. Cyber operations are part of every modern nation’s arsenal now.
Manoj Tandon: Let’s talk about your book, The Art of Cyberwarfare.
Jon DiMaggio: That book draws on my years chasing nation-state actors. The first half is storytelling—real cases showing why attribution matters. Many people ask, “Why does it matter who hacked us?” But knowing your adversary shapes your defenses. The second half teaches technical attribution—how to analyze indicators, correlate data, and use open-source methods to identify threat actors. It’s written for both professionals and enthusiasts. I’m also working on The Art of Attribution, a report applying my framework to complex modern cases like BlackCat. And eventually, I’d like to write a full book on ransomware and human intelligence.
Manoj Tandon: That would be a must-read. One quick clarification—was the Sony hack really North Korea?
Jon DiMaggio: Yes. The 2014 attack was North Korea. There have been other unrelated Sony breaches since—like RansomVC last year—but the original one was definitely DPRK.
Manoj Tandon: Got it. John, this has been a phenomenal conversation. Thank you for being so generous with your time—and please come back when your next research or book drops.
Jon DiMaggio: Thanks, Manoj. I’d be happy to.
Manoj Tandon: Take care, John.
Jon DiMaggio: You too.
Read more about Jon on his LinkedIn
Get Jon’s Book ” The Art of Cyberwarfare” here
Check out the other episodes in Season 17:
Ep. 0 Jon DiMaggio – Tracking Cyber Criminals
Ep. 1 John Carse – Why Your Browser Is Your Biggest Risk
Ep. 2 Alex Sharpe – Is Your Job Safe From AI?
Ep. 3 Chuck Brooks – Thinking Beyond the Checkbox
Ep. 4 Henrik Parkkinen – Adapting to AI & Rethinking What We Protect
Ep. 5 Alex Sharpe – Are AI Models Being Trained with Lies?
Ep. 6 Santosh Kaveti – Disaster Recovery Isn’t Optional
Ep. 7 Bob Burke – Think MFA is Enough? Think Again.
Ep. 8 Ed Gaudet – The Biggest Mistakes in Healthcare Security
Ep. 9 Husam Shbib – The Hacker’s Playbook
Ep. 10 Shayla Treadwell – The Psychology Behind Cyber Resilience
About Jon DiMaggio
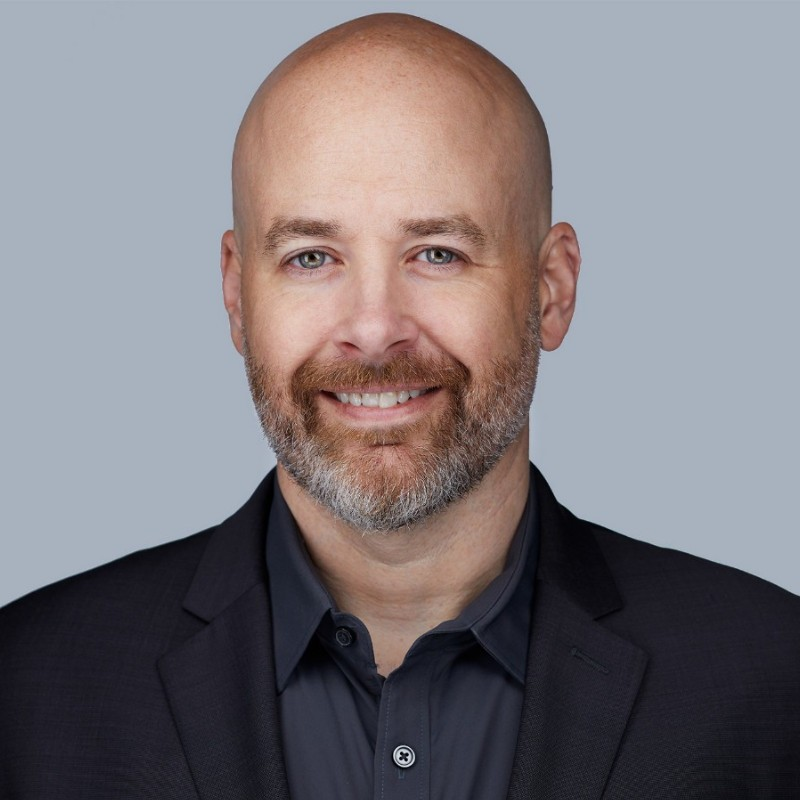
Jon DiMaggio is the chief security strategist at Analyst1 and has over 15 years of experience hunting, researching, and writing about advanced cyber threats.
As a specialist in enterprise ransomware attacks and nation-state intrusions, including the world’s first ransomware cartel and the infamous Black Vine cyberespionage group, he has exposed the criminal organizations behind major ransomware attacks, aided law enforcement agencies in federal indictments of nation-state attacks, and discussed his work with The New York Times, Bloomberg, Fox, CNN, Reuters, and Wired.
You can find Jon speaking about his research at conferences such as RSA and Blackhat.
About Us
Dark Rhiino Security’s Security Confidential is a weekly Cybersecurity podcast where Host, Manoj Tandon, talks to Infosec and Cybersecurity professionals about the current issues going on in our industry. Guests are able to share their stories about how they began their journey into cybersecurity and connect with our audience. Listeners are able to tune in through Spotify, Apple Podcasts, Google Podcasts, Amazon Music, iHeartRadio, Youtube, LinkedIn, and more.
For inquiries, please email media@darkrhiinosecurity.com
Share and spread the word!
Archive source: Original website record. Original wording and artwork retained.