
SECURITY CONFIDENTIAL
Security Confidential S15 E8 Dan Lohrmann
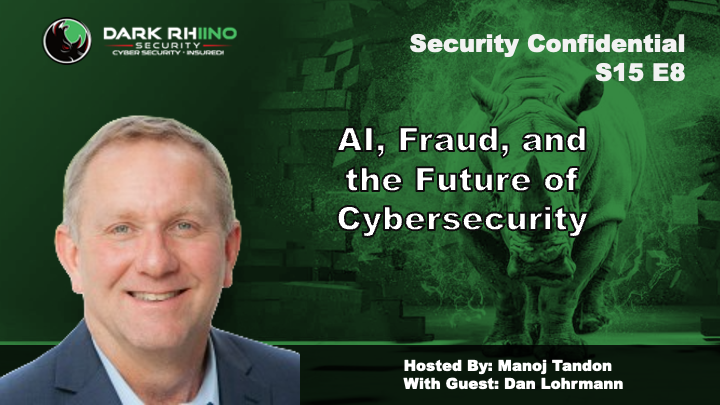
This week on Dark Rhiino Security’s Security Confidential podcast, Host Manoj Tandon talks to Dan Lohrmann, an internationally recognized cybersecurity leader, keynote speaker, and author with over 30 years of experience. He served as Chief Security Officer, CTO, and CISO for Michigan’s government and received numerous national awards, including CSO of the Year and Computerworld Premier 100 […]
Video
This week on Dark Rhiino Security’s Security Confidential podcast, Host Manoj Tandon talks to Dan Lohrmann, an internationally recognized cybersecurity leader, keynote speaker, and author with over 30 years of experience. He served as Chief Security Officer, CTO, and CISO for Michigan’s government and received numerous national awards, including CSO of the Year and Computerworld Premier 100 IT Leader. He has advised top-level government and business leaders, including at the White House and U.S. Department of Homeland Security. Currently, Dan is the Field CISO for Presidio and co-author of Cyber Mayday and the Day After, a guide for managing business disruptions.
AI, Fraud, and the Future of Cybersecurity | Security Confidential
Chapter Titles:
00:00 Intro
01:59 Our Guest
09:13 Was Cybersecurity a term back then?
13:05 Everybody keeps getting breached, Why?
19:00 Creating a culture
32:50 Trust but Verify mentality
45:53 Stopping Online Fraud
52:13 Bring your own AI
57:05 Cyber Mayday
Audio:
Spotify Embed: S15 E8 AI, Fraud, and the Future of Cybersecurity
Important Links:
Transcript
Manoj Tandon (00:01.591)
Hello everyone, this is your host, Manoj Tandon. Welcome to another episode of Dark Rhiino Security’s Security Confidential. And today we are honored to have Mr. Dan Lohrman join us. Dan is an internationally recognized cybersecurity leader, keynote speaker, and author with over 30 years of experience. He has been the chief security officer, CTO, and CISO for the government of the state of Michigan. And we’re going to talk a little bit about that.
Dan Lohrmann (00:25.587)
And CISO for the government of the state of Michigan.
Manoj Tandon (00:31.612)
That must’ve been an interesting adventure. Also, he is the co-author of Cyber Mayday and The Day After, a guide for managing business disruption. Dan, we are honored to have you. Thank you so much for joining.
Dan Lohrmann (00:35.942)
Manoj, it’s wonderful to be with you. I’m really looking forward to the conversation today. So thanks for having me.
Manoj Tandon (00:55.723)
Hey, so, you know, we were gonna begin with the origin story because as we’ve learned from cybersecurity, everybody came from someplace else. Very rare do we get people who are computer science majors in college that were focused. So please give us a little bit of a…
Dan Lohrmann (01:16.654)
Yeah, well, I’m gonna be your exception because I was a computer science major in college. And I actually got my master’s at Johns Hopkins in computer science. My first job out of college—I went to Valparaiso University, played quarterback on the football team—that was a long time ago, in the eighties, very different times. Reagan was still president.
My first job out of college was at the National Security Agency. So it was a great way to start my career. I was at NSA for six years. We used to say security is our middle name, and there were posters everywhere—“someone is watching you”—and they were watching you. It was great though. I loved it. It was all about networks worldwide.
My focus there in my early days was networking. Security was part of everything you did. Everything was secure, encrypted, top secret. But we built worldwide networks before AOL built a worldwide network. Then I moved to England, stayed in the intelligence community, and worked on a US-UK military base for seven years with Lockheed Martin and ManTech International doing computer networks, building fiber networks and connectivity.
Then the big change—I went back to the state of Michigan.
Manoj Tandon (03:05.591)
That is a swap from England all the way back to the Midwest.
Dan Lohrmann (03:11.192)
It was. It was a family situation. My wife was from Michigan. I was born and raised in Baltimore, Maryland. We decided we needed to move back. I didn’t know anything about Michigan at the time. I literally drew a circle around Ann Arbor and said I need to be within an hour of here.
I got a job as CIO for the Department of Management and Budget during the Y2K years.
My first day on the job was a dramatic change. I walked into the building—no security, no guards—but signs everywhere saying “watch your purse.” People were walking in off the street stealing purses. Three were stolen the week before. When I brought up security, people laughed and said, “we’re not NSA now, are we?” It was all about Y2K compliance.
After 9/11, everything changed. We had built e-government services, but security was lacking. After 9/11, we created a centralized enterprise-wide security office, and that’s how I became the first CISO for the state of Michigan.
Manoj Tandon (06:09.823)
Was security on networks a concern back then, or was it just a closed system?
Dan Lohrmann (07:08.414)
Everything was encrypted. It was also a closed system. You had to be in secure facilities to access data. You couldn’t take work home—it was all classified.
Manoj Tandon (08:13.567)
Was cybersecurity even a term back then?
Dan Lohrmann (08:16.9)
No, it was called information security or information assurance.
Manoj Tandon (11:56.939)
Why do you think cybersecurity fails so often?
Dan Lohrmann (12:48.934)
Great question. First, it’s about people, process, and technology—but mostly people. Attackers go after the weakest link. We have to be right every time; they only need to be right once.
Second, crime has always existed. Just like bank robberies, cybercrime won’t disappear.
Third, technology is accelerating both good and bad outcomes. As innovation increases, so does exploitation.
Manoj Tandon (20:32.602)
How do you create a culture of cybersecurity?
Dan Lohrmann (20:32.602)
I’ll tell you a story. Early in my career, I was “Dr. No.” I blocked Wi-Fi adoption because of security concerns. My boss told me: “If that’s your answer, you can’t be the CISO.” She gave me a week to figure it out.
We studied how others did it, implemented secure Wi-Fi, and later won a national award.
The lesson: you must get to yes securely. Don’t just say no—offer solutions.
Manoj Tandon (28:13.479)
How do you deal with users prioritizing convenience?
Dan Lohrmann (28:52.862)
You can’t just block everything. You need alternatives and secure pathways. People will find ways to do their jobs regardless.
Manoj Tandon (31:10.839)
How do you educate users effectively?
Dan Lohrmann (31:49.958)
Make it engaging—short, interactive, gamified. Go where people are. Use real stories.
We had a nurse who caused a data breach but became our best security ambassador. People listened to her because she had lived it.
Manoj Tandon (44:17.606)
What about online fraud?
Dan Lohrmann (44:17.606)
The FBI is focusing on awareness and reporting. Fraud includes scams like phishing, Ponzi schemes, and impersonation attacks. The key advice: be cautious, verify independently, and report incidents.
Manoj Tandon (50:46.497)
What about AI risks?
Dan Lohrmann (52:01.604)
You need governance and guardrails. You can’t just ban AI—people will use it anyway. Use tools that monitor and control access, prevent sensitive data leaks, and enable secure usage.
Manoj Tandon (55:15.135)
Anything you’d like to plug?
Dan Lohrmann (55:23.334)
My book Cyber Mayday and the Day After—it’s about real ransomware stories and how leaders respond. Also, feel free to connect with me on LinkedIn and check out my blog, Lohrmann on Cybersecurity.
Manoj Tandon (56:54.785)
Dan, you’ve been fantastic. Thank you so much.
Dan Lohrmann (57:11.75)
Thank you for having me.
Manoj Tandon (57:13.16)
Thank you. We look forward to the next time.
Dan Lohrmann’s Articles
Kiteworks enables organizations to effectively manage risk in every send, share, receive, and save of sensitive content. To this end, they have created a platform that delivers content governance, compliance, and protection to customers. The platform unifies, tracks, controls, and secures sensitive content moving within, into, and out of their organization, significantly improving risk management while ensuring regulatory compliance on all sensitive content communications.
Check out the other episodes in Season 15:
Ep.0 Robert Kerbeck – Fame, Fortune, and Corporate Espionage
Ep. 1 Stephen Kowski – Inside the mind of a Field CTO
Ep. 2 Vivek Ramachandran – Inside Email Security: Breaking Through Gmail and Outlook’s Defenses
Ep. 3 Dr. Eric Daimler – AI’s Future: More Than Just Machine Learning
Ep. 4 Purandar Das – Data is the New Oil
Ep. 5 Aaron Painter – Understanding Deepfakes
Ep. 6 Jake Moshenko – Navigating Open Source and Distributed Systems
Ep. 7 Nick Espinosa – Why CISOs Must Master Nerd to English Translation
Ep. 8 Dan Lohrmann – AI, Fraud, and the Future of Cybersecurity
Ep. 9 Greg Schaffer – How the Role of a vCISO is changing
Ep. 10 Sanjay Chopra – AI Innovations and the Future of Automation
About Dan Lohrmann
Dan Lohrmann is an internationally recognized cybersecurity leader, keynote speaker, and author with over 30 years of experience. He served as Chief Security Officer, CTO, and CISO for Michigan’s government and received numerous national awards, including CSO of the Year and Computerworld Premier 100 IT Leader.
He has advised top-level government and business leaders, including at the White House and U.S. Department of Homeland Security.
Currently, Dan is the Field CISO for Presidio and co-author of Cyber Mayday and the Day After, a guide for managing business disruptions.
About Us:
Dark Rhiino Security’s Security Confidential is a weekly Cybersecurity podcast where Host, Manoj Tandon, talks to Infosec and Cybersecurity professionals about the current issues going on in our industry. Guests are able to share their stories about how they began their journey into cybersecurity and connect with our audience. Listeners are able to tune in through Spotify, Apple Podcasts, Google Podcasts, Amazon Music, iHeartRadio, Youtube, LinkedIn, and more.
For inquiries, please email media@darkrhiinosecurity.com
Share and spread the word!
Original podcast listings
Archive source: Original website record. Original wording and artwork retained.