
SECURITY CONFIDENTIAL
Security Confidential S1 E3 Tyler Smith
This week on Dark Rhiino Security’s Security Confidential podcast, Manoj Tandon is joined by Tyler Smith, co-founder of Dark Rhino Security and a seasoned cybersecurity practitioner with extensive experience in building and operationalizing security programs. Tyler Smith and Manoj Tandon discuss how organizations can help the C-suite understand, value, and even fall in love with cybersecurity. Rather […]
Audio
This week on Dark Rhiino Security’s Security Confidential podcast, Manoj Tandon is joined by Tyler Smith, co-founder of Dark Rhino Security and a seasoned cybersecurity practitioner with extensive experience in building and operationalizing security programs. Tyler Smith and Manoj Tandon discuss how organizations can help the C-suite understand, value, and even fall in love with cybersecurity. Rather than treating security as a backroom IT expense, they explain why cybersecurity should be viewed as a business problem, a risk-management function, and a strategic driver of revenue, margin, customer experience, and operational resilience. From FAIR-based risk quantification to identity management, data protection, healthcare collaboration, and customer insights, this conversation reframes cybersecurity as a business enabler.
Spotify Embed: S1 E3 C-Suite: How to fall in love with cybersecurity
Chapter Titles
00:00 Intro
00:13 Why the C-Suite Should Care About Cybersecurity
1:25 Using FAIR to Quantify Cybersecurity Risk
05:22 How Cybersecurity Can Increase Revenue and Margins
06:41 Identity, IAM, and Customer Data as Business Assets
21:51 Cybersecurity as a Strategic Advantage in Healthcare and Beyond
Important Links:
Connect with Tyler on LinkedIn
Transcript
Tyler Smith: Welcome to Security Confidential by Dark Rhino Security, where we get together and talk about all things information security. I’m Tyler,
Manoj Tandon: And I’m Manoj Tandon
Tyler Smith: Today we’re going to talk about how to make your C-suite fall in love with security. There’s a lot of things that motivate the C-suite to invest in security. I’d say probably the biggest one is they’re smart enough to know that they have to.
Manoj Tandon: That’s right. In fact, some industries have mandated that cybersecurity risks be brought up to the board level. So if you look at the insurance industry, their regulatory councils have mandated that those risks be reported to the board of directors at least on an annualized basis, which converts cybersecurity very much from a technical problem to a business problem, which is what it truly is. It’s often bucketed in the world of backroom IT, but it’s not that. It’s actually a business problem that has a direct correlation to the functioning of the company, management of risk, and ensuring business continuity under unfavorable circumstances. Now the insurance industry at least has taken it upon itself to make sure that that mandate is somewhat clear, and other industries have taken up similar requirements. There are a number of different ways that you can approach security, but a risk-based approach that ties the actual problems a company faces to dollar amounts is a very good method of doing it. It allows you to prioritize the issues.
Tyler Smith: That’s exactly right, Tyler. I think getting a common language that everybody understands in front of the executive team is a key way to getting them to understand cybersecurity. Too often it is brought up in arcane terms to them that they don’t really follow. But at Dark Rhino, for example, we follow the FAIR methodology, which is the Factor Analysis of Information Risk. It’s a formal approach that in detail formalizes the quantification process of risk. And those risk values, the continuum of risk from various threat vectors that the business faces, is something that any executive will understand and any financial person will understand. That really allows for a good objective discussion and a prioritizing of projects and spending of capital dollars where it’s needed. There are several others out there, but at Dark Rhino, that’s what we follow and we’ve seen great results from that. It provides a common language. Think about it this way: if I come to you and I say, “Hey, you have a threat from some ransomware virus, malware, Trojan, or some other piece of technology out there,” you may not even know what the implications of that really mean. Whereas if you came in and said, “Hey look, we have a likely loss of $700,697 per malware event, and we have some exposure from malware from the way we are running our returns program in the company if I’m a retailer, or the way in which we are handling contractors,” which one do you think is going to make more sense? One requires context from a technical level and an understanding of the daily changing threat landscape that’s present in the cybersecurity world. Whereas the other just requires an understanding of financial implications, potential legal implications, and potential reputational loss implications, which is something that’s Business 101 that everyone would understand, and that’s what FAIR brings to the table.
Manoj Tandon: That’s absolutely right, Mann. It’s something that takes it from complex technical understandings to financial understandings, and you can even review solutions to see which one would be the best solution in a similar manner, looking at the cost versus the amount of risk reduced. To really make a risk presentation, you have to have a sound foundational understanding of business operations first, and that comes with time. It comes with experience.
Tyler Smith: Yeah, I agree. Business is something that, from a technical person’s standpoint, speaking for myself, took me a little while to realize. There’s more to it than just the nuts and bolts of the technology that we have to employ to provide proper security. It’s very much driven by the business side of things, and that comes with experience. You know, the key part is: where do you spend limited capital or expense dollars? And where you have to do this is where your risk goes. But I think that’s a fairly mundane conversation because if I listen to any number of security podcasts that are out there, everybody wants to talk about risk in some way, shape, or form. It seems to be the new industry pet word. What I don’t ever hear discussed is this question. Tyler, I’d like to bring some of this up with you and maybe you can lend some insights on this. How do you use cybersecurity to actually increase margin contributions and increase revenue to the organization? It’s a topic that is not very widely discussed because it’s not the interesting thing that everyone focuses on. Security is security for the sake of security, if we’re being honest.
Manoj Tandon: Yeah, that’s right. I agree with you completely. Companies focus on security for the sake of security. And they do totally. They have a CISO, and then the CISO is mandated to secure their operations, right.
Tyler Smith: Yeah, and nobody goes into the discussion asking, “Okay, how are we going to increase our capabilities with security?” It’s always about how we’re going to stop threats. With a lot of the older technologies, if you sat there and wondered how we were going to increase our capabilities with this, it wouldn’t apply. It’s not really applicable with older technologies. Some of the newer technologies that are coming out, things like Okta, can actually improve your capability and as a result improve your bottom line.
Manoj Tandon: You know what, Tyler, that’s a really good one because you brought up Okta, and I was going to generalize it a little bit and say the world of identity is a great place for any organization regardless of the business that they’re in. Whether they are selling orange juice or they’re selling batteries or insurance or they’re a bank or they’re a medical office, it doesn’t really matter. The world of identities and the technologies that govern identity that are used by cybersecurity professionals by firms like us in securing the environment can equally play a huge role in furthering marketing programs. So if you look at empires that have been built by Facebook and Google, where the perception is that it’s all free and the consumer is used to that free environment, in reality, the consumer is the product. It is their identity and their patterns of behavior that are the real product and the valued asset for those companies.
Tyler Smith: And the identity piece for that is central to their business. The way that a normal company that isn’t Facebook would benefit from something like Okta is to think about all the times that are wasted trying to get new people on board. For example, with Okta, your provisioning time goes down, your security increases, and your people become more flexible with how they can request access to applications. At the same time, it’s more secure. There’s oversight and auditability for those requests, and a process can be built that can take people from sitting and waiting to working much faster than you traditionally could have done. I’ve experienced this numerous times at different companies that I’ve gone to work as a contractor at. I get there and they’re like, “Oh, we’re super excited to have you. We don’t have a laptop for you yet.” A week goes by and I still don’t have a login. Then maybe I finally get the login, but I still have zero access to my applications because those are tied up in some tedious approval process. Meanwhile, I’m billing out at X number of dollars an hour, and your people are just kind of waiting around for someone to click buttons so I can get access to things. With Okta, you can automate that process, ensure that it’s secure, and you have the added security that it builds into your authentication process for new and legacy applications. Okta basically allows your people to be more effective and timely while being more secure. It’s just one example.
Manoj Tandon: I want to extend this concept to the 100,000-foot level. You’re right, Okta is a technology and it does help in managing identities, but when we are looking strategically, how do we want to use these cybersecurity technologies? Let’s make up an example. Let’s say I’m a company selling golf balls, because I’d rather be golfing today, but I can’t. In that industry, there’s a lot of contract manufacturing. There have been a lot of mergers and acquisitions over time. If you look at that landscape where you have grown by acquisition and you have multiple divisions, in this case you might sell everything from golf balls used by professional players to specialty balls used at ranges to balls used by more amateur players as a learning device that may not even be legal on a regulation course. In such a landscape, you might have one person—your customer—who might have registered in times past with all these various companies that you acquired. They might have registered with different emails or different name truncations for their loyalty program so that they get coupons in the email for Dick’s Sporting Goods. As these acquisitions happened, those identities never got consolidated, right? So now, one of the biggest things for marketing would be: how do I do cross-brand selling? How can I structure promotions that would appeal to a consumer that’s registered with brand one, brand two, and maybe even brand three? What has been their purchasing pattern? That data may exist in the individual silos that represented those companies, but it doesn’t exist in a consolidated fashion. Today, the big word is “Big Data,” pun intended. People will instantiate multi-million dollar projects because it’s the “in” thing to do. They will try and create a data lake and then they’ll build heavy analytics. There is a time and a place for that—I’m not completely against that approach. But a much simpler approach that would give you results now would be a program in which you consolidate those identities across all those lines.
Tyler Smith: Oh yeah.
Manoj Tandon: Once you do that, now you can track buying patterns across the brands from a single identity. It doesn’t matter what loyalty card that person is using or how they log in because you know ultimately Mr. X is the same guy as Mr. Y. They are exactly the same person, right? And you can market to them specifically. You can create unique pricing for them, which is something that Amazon does very effectively. If I log into Amazon to look for a product, and you log in for that product, and Senna logs in, we may all be presented with three different prices for the exact same product because they know how much it means to me and how little it might mean to you, Tyler.
Tyler Smith: Right. Exactly.
Manoj Tandon: But you have to know that identity first to be able to do that. And that’s something that a good strategy with Identity and Access Management as a foundation—which may be built on a tool like Okta or perhaps any other tool—can provide. If it’s implemented correctly, you can do a consolidation. That consolidation has real material value. For example, in a retailer, it can impact your rates of return. You can identify who’s abusing your return policies and say, “This guy always orders a hundred bucks’ worth of golf balls just so he can get free shipping, and then he returns nine of those boxes.”
Tyler Smith: Yeah.
Manoj Tandon: So the company takes a hit on the nine boxes that were returned and pays for the return shipping. Stop offering the guy free shipping.
[laughter]
Manoj Tandon: You don’t need a big data program to do that. What you need is a good identity-based program that tracks these patterns and can really have a material impact on the bottom line. You affect the rates of return and you definitely affect the margin contribution.
Tyler Smith: Oh, definitely. Definitely. And the example you gave brought up another thing that I’ve seen as a consultant: companies that are made of many little companies through acquisition, or through a decision to create a new division because their effort was different or regional. They have duplicate efforts at identifying their people and they never sought to consolidate their employee identities. So onboarding, offboarding, and getting people to work across business units or entities within the same corporation can be very difficult for these companies. The issue that they often have is they’ll end up having a dozen different efforts doing the same thing. Any one of which could be applied to the entire body as a whole to control access to resources. That happens a lot.
Manoj Tandon: Tyler, that’s a very good point. In fact, Harvard Business Review many years back—I remember reading an article on mergers and acquisitions—cited an incredible number. I think it was north of 70% of these mergers and acquisitions become failures over the long run, where they ultimately lead to divestitures or some form where the value creation that was imagined just doesn’t take place.
Tyler Smith: Right.
Manoj Tandon: Perhaps what you are alluding to is a significant contributing factor.
Tyler Smith: I think it definitely is. The problem occurs when companies fail to plan on how they’re going to integrate the technologies. They just look at the books, the operations, and the marketing, and create plans for those things. Many times they just assume that IT is going to figure it out. We just want them to keep doing what they’re doing; we’ll deal with that later. Some do include it in the process, but they’re very timid about their approach. Instead of saying, “We’re going to stand up a second system,” and migrate some of the users over to that new system. When it doesn’t break everything, or if it does, we’ll fix it. But once we have it figured out, we’re going to move everybody and decommission the other system. I see that very infrequently. And when I do see it, it’s usually a 5-year or 10-year plan that is unnecessarily cautious. They ignore the fact that it’s not that hard to stand up a new system, make sure that it functions, move some people over, and then move everyone over once everything works.
Manoj Tandon: Tyler, it isn’t hard, but what you’re fighting is human nature.
Tyler Smith: Absolutely.
Manoj Tandon: That is an age-old problem that people get paid a lot of money to try and affect, but it’s a problem of company culture and it is a beast to tackle. Now, one thing that is happening as technology has become much more prevalent in the propagation of goods and services: the rate of change has become really fast, and some of these larger companies that have been battleships in the marketplace for a long time are facing very healthy competition from players that are much more nimble. That’s been time immemorial. If we turn back the clock to the 1900s, we would find that example in automotive, where at one time there were 400 automotive companies in the United States and now we’re left with three.
Tyler Smith: Yeah, just variations of the same.
Manoj Tandon: But what is happening is the consumer is becoming much more educated. The rate at which the consumer is learning and becoming self-driven to find products is something new that I don’t know a lot of companies are prepared for. Running sales here at Dark Rhino, the old model of sales still employed by a large number of tech companies is a direct sales model where you have an account exec that is directly marketing to one account, right? Using all the tools of the trade that have been established. But what we’ve seen with buying patterns, especially in our sector which is high technology and rapidly changing, is that people don’t want to be sold. They want to discover a solution. They want to be educated. Sales has really gone from carrying a bag and saying, “Hey, I got this,” to an educational exercise. If you educate the consumer and, most importantly, do it in a fashion that allows them to look at potential new approaches to an old problem—like we’ve been talking about with consolidation of identities to increase margins—then you might actually make the sale. You’ve given them a new approach that they may not have thought of, and at that point you have the credibility. Other people are not talking about it, and that gives them a competitive advantage. That’s what they are ultimately looking for. Security doesn’t make a company run. It’s their competitive advantage in whatever field they operate in that makes a company pay its employees and pay the bills. As security professionals, if we can enlighten them with a different approach to apply the same technology and end up with great compliance but also give them a competitive advantage, that’s a huge win. You can apply that model across everything, and that’s changing the way in which we sell dramatically.
Tyler Smith: Yeah. It’s using people’s own intelligence to help sell something they already know they need, but they don’t quite understand it or maybe they don’t even realize they need it. When you combine it with their experience and intelligence, they go, “Well, yeah, that actually would make sense here. I can see how it would improve what we already have.” As opposed to just listing off benefits, it’s more specific. You’re educating them on how it works and they’re making the decision. Yes, I see how that would benefit us specifically. It is shifting heavily. Identity is just one example of something that could help someone further their business. Endpoint Detection and Response is another one that can help. If your people’s machines are working more than they’re broken, and you’re protecting them from doing something that would break the machine, it’s going to impact your bottom line. If your $100,000-a-month sales guy is selling his butt off and his laptop gets malware on it, guess what he’s not doing while he’s waiting for somebody to fix it or replace it? He’s not selling, not at the same level. For that matter, I guess you could say it’s not just endpoint protection, but I would also throw in all your Data Loss Protection technology. If we make that corporate data available to anyone at any time, and it’s not sitting on a localized environment, then it can be utilized. If we build our processes in the company that can leverage that information, then the individual becomes a lot less of a factor if there’s a data loss event or some kind of a mechanical shutdown of their device.
Manoj Tandon: Right. Or if it’s lost or stolen.
Tyler Smith: Right. And the security tools that are available can be leveraged to add that kind of safeguard and capability. Data being available to people is a very good thing from a business perspective. Traditional security says that’s not necessarily a good thing; it can be a really bad thing. With the current technologies like Bitglass or Code42, you have the ability to be very open and protected at the same time. Previously, that wasn’t the case; it was either open or it was protected. Now we have the ability to apply intelligent tools to provide a solution that is as open as it should be while maintaining a level of security that exceeds what was previously available with traditional methods of blocking people. I’m excited to see where things are going to go because it’s already changed in less than five years.
Manoj Tandon: Openness is going to play a huge factor in healthcare. A lot of these EMR systems are fairly antiquated technologies and they were not built in an era where openness and sharing of patient information was a high priority.
Tyler Smith: Right.
Manoj Tandon: But as we transition—albeit very slowly—to outcome-based medicine, it becomes very necessary for that patient information to be shared with medical collaborators. In fact, we at Dark Rhino have several small physician practice groups with only five or six doctors that use Okta to securely input patient information in a very secure environment. It’s HIPAA compliant and has all the certifications and controls. They are able to share that information with outside medical collaborators and they’re able to track it. It’s auditable. They know who saw it and where it was sent. It meets all the compliance standards, but most importantly, it allows them to openly communicate with other physicians, practitioners, and scientists on a specific problem, which is better for the patient’s overall outcome.
Tyler Smith: Yes, it is, which is better for the overall bottom line, especially given the new measurements used to determine how reimbursement will be handed out via government funding. Those are heavily tied to patient experience, and wait time is heavily tied to patient experience. So being able to share very quickly but also very safely is going to increase the ability to get better returns. It doesn’t matter if you’re a small doctor’s office or a large medical practice; the C-suite would probably be interested in knowing that this capability is out there. It checks all of those boxes that take care of risk and operational capabilities as well.
Manoj Tandon: And that is exactly the topic of this podcast. Hopefully, people have gotten food for thought here. We could probably discuss this ad nauseam. There are so many use cases. If you are in business, don’t think of cybersecurity technologies as a means by which you just secure the environment, but really start looking at them through the lens of risk. And maybe even more importantly, look at them strategically as to how the capabilities they provide can truly impact your bottom and top lines, and your overall customer experience.
Tyler Smith: Well, thank you for coming today.
Manoj Tandon: Absolutely.
Tyler Smith: Yeah, and thank you guys for listening. We will include some resources in the show notes, so check those out. Also, please subscribe to our podcast and we will see you guys next time. Bye everyone.
Tyler Smith: Should be while maintaining a level of security that exceeds in some cases what was previously available with traditional methods of blocking people from using or accessing data or sharing data. It’s just I’m I’m excited to see where things are going to go with that because it’s already in less than 697 years.
Manoj Tandon: Openness. If you look at another industry that comes to mind where this is going to play a huge factor is healthcare, right? So if we look at a lot of these EMR systems are fairly antiquated technologies and they were not built in an era where openness and sharing of patient information was was a high priority if you will.
Tyler Smith: Right but now if we are transitioning albeit very slowly but as we transition to outcome-based medicine more then it becomes very necessary for that patient information to be shared with medical collaborative collaborators. And in fact, we at Dark Rhino have a small several small physicians practices groups that are only maybe five or six doctors that use the technology of Bach to securely and put patient information in you know and it’s a very secure environment. It has it’s HIPPA compliant uh has all the certifications and controls for that and then they are able to share that information with outside medical collaborators and they’re able to track it. It’s auditable. They know who saw it, where it was sent. It it meets all the compliance standards but most importantly it allows them to openly communicate with other physicians and practitioners and scientists on a specific problem and that is better for the patients overall outcome.
Manoj Tandon: Yes. Yes, it is. which is better for the overall bottom line, especially given the new measurements used to determine how reimbursement will be handed out via government funding. Those are heavily tied to patient experience and wait time is heavily tied to patient experience. So being able to share very quickly but also very safely is going to increase the ability to get better returns. If you are and and that doesn’t matter if you’re a small doctor’s office or if you’re a large medical practice the suite would probably be interested in knowing that this capability is out there. It checks all of those boxes that take care of risk and it in it checks boxes that take care of operational capabilities as well.
Tyler Smith: And that is exactly the topic of this podcast right hopefully people have gotten food for thought here I mean we could probably discuss at nauseium there are so many use cases if you are in business then don’t think of cyber technology cyber security technologies as a means by which you just secure the environment, but really start looking at them through the lens of risk. And maybe even more importantly, look at them strategically as to how the capabilities that they provide can truly impact your bottom, top lines, and your overall customer experience.
Manoj Tandon: Well, thank you for coming today.
Tyler Smith: Absolutely.
Manoj Tandon: Yeah. And thank you guys for listening. For more information on we will include some resources in the show notes. So check those out. Also please subscribe to our podcast and we will see you guys next time. Bye everyone.
Check out the other episodes in Season 1:
Ep. 0 DRS Team – Cybersecurity Conferences
Ep. 1 Luis Martin – Artificial Intelligence
Ep. 2 Stefan Ludlow – Personal Responsibility in Cybersecurity
Ep. 3 Tyler Smith – C-Suite- How to fall in love with Cybersecurity
Ep. 4 Jordan Fulk – Bourbon and IT Talent
Ep. 5 Tyler Smith and Manoj Tandon – Zoombombing, Privacy, and Working from home
Ep. 6 Mitch Spaulding – Alternative Paths to a Cyber Career
Ep. 7 Karen Hough – How to build resilience, adapt to obsticles, and thrive
Ep 8. Dakota Rae – Swim with Sharks and Thrive
Ep. 9 Tyler Smith – Tips on Implementing EDR
Ep. 10 Chris Cazel – Learning Okta
About Tyler Smith
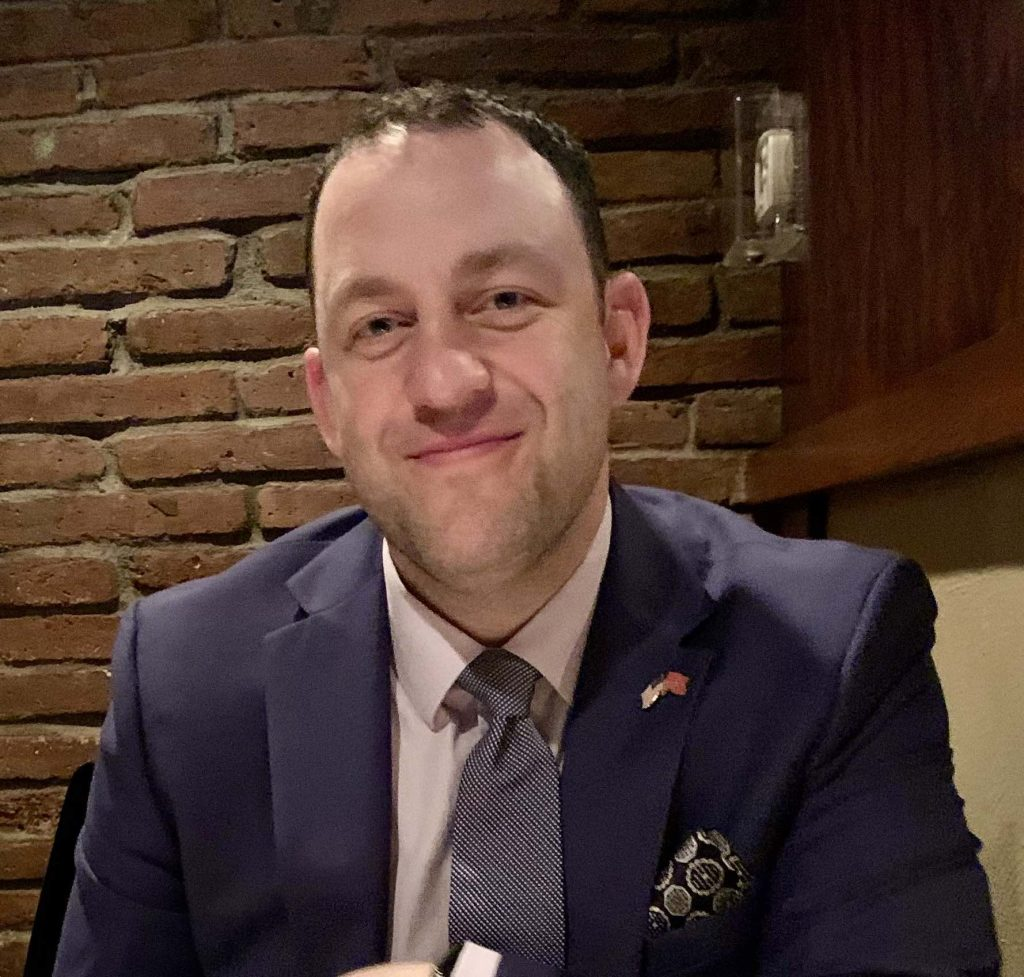
Tyler Smith, co-founder, CTO, and President of Dark Rhiino Security Inc., a leader in the computer security industry. Tyler shares insights from his journey building three successful companies, including valuable lessons from his experience leading Dark Rhiino.
He is a veteran of the US Marine Corps, where he served as an Infantry Rifleman and deployed to multiple countries in support of the Global War on Terror. He studied Political Science and International Studies, Security and Intelligence at The Ohio State University. He has worked in security and technology since 2011 and has worked in technical roles for Apple Inc., Ohio Health, Reid Elsevier Technology Services/Lexis Nexis, Toyota, Federated Investors, Honda of America Mfg, to name a few.
About Us:
Dark Rhiino Security’s Security Confidential is a weekly Cybersecurity podcast where Host, Manoj Tandon, talks to Infosec and Cybersecurity professionals about the current issues going on in our industry. Guests are able to share their stories about how they began their journey into cybersecurity and connect with our audience. Listeners are able to tune in through Spotify, Apple Podcasts, Google Podcasts, Amazon Music, iHeartRadio, Youtube, LinkedIn, and more.
For inquiries, please email media@darkrhiinosecurity.com
Share and spread the word!
Original podcast listings
Archive source: Original website record. Original wording and artwork retained.